KSC Readiness Audit – Cybersecurity and NIS2

Why do you need this service?

KSC readiness audit – scope first, then implementation

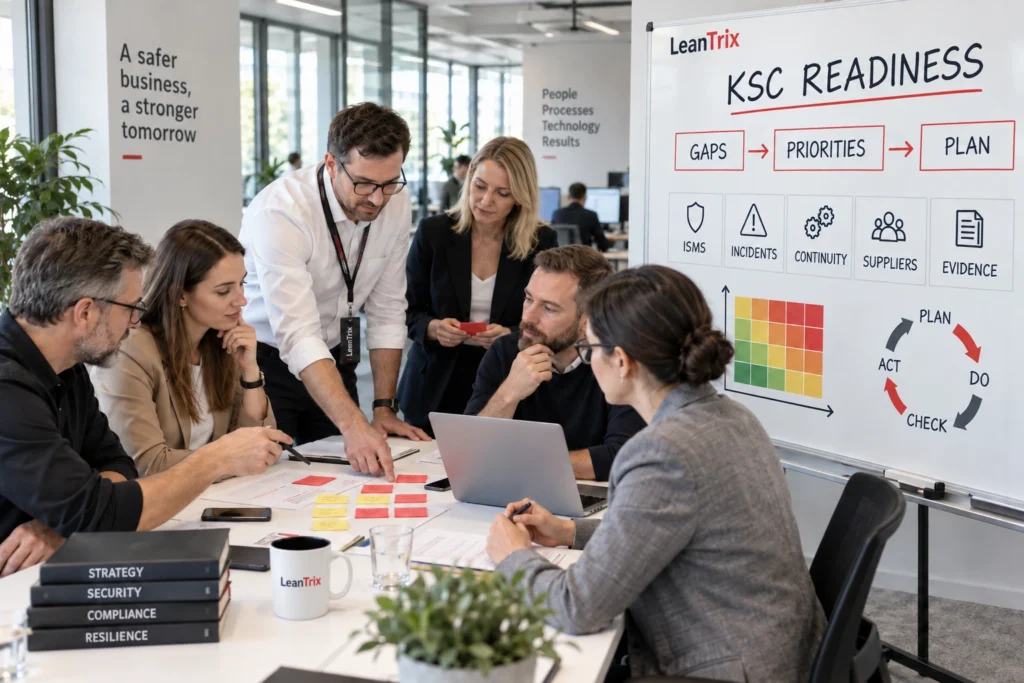
A KSC readiness audit is a voluntary assessment of an organisation’s readiness for KSC and NIS2 requirements. Before procedures and IT projects are created, we answer three specific questions.

Does KSC apply to us?We establish the organisation’s status, service scope and applicable deadlines.
Where are the gaps and risks?We compare requirements with actual processes, systems, suppliers and evidence.
What should we do first?We establish priorities, action owners and a feasible implementation roadmap.

The amendment to Poland’s National Cybersecurity System Act (KSC) implements NIS2 requirements into Polish law. Obligations extend beyond documentation and IT: they cover management accountability, the ISMS, risks, suppliers, incidents, business continuity, training and evidence of effectiveness.

The scope may include manufacturing, energy, transport and logistics, digital and ICT infrastructure, healthcare, water and wastewater, waste management, public administration and research organisations. Sector name alone does not determine applicability. Services, size, legal form, related entities and specific statutory criteria matter. Read the full KSC and NIS2 guide for organisations (in Polish).

We do not begin by copying procedures. We first agree the service scope, dependencies and risks, then design an ISMS and actions that work in the actual organisation.

What do we examine during the audit?

  • Status, scope and deadlines – the entity’s classification and regulated services.
  • Services and dependencies – processes, IT/OT systems, data, assets, locations and suppliers.
  • Governance and the ISMS – management roles, risk owners, policies, measures and reviews.
  • Safeguards and the supply chain – access, assets, vulnerabilities, changes, monitoring, cloud and outsourcing.
  • Incidents and continuity – detection, escalation, communication, BIA, BCP, backups and recovery tests.
  • People and evidence – training, cyber hygiene, operational records, test results and management decisions.

Readiness audits, statutory audits and ISO 27001

  • A readiness audit is a voluntary assessment producing a gap and risk map and a roadmap.
  • A statutory KSC audit is a formal, independent assessment performed in cases specified by Polish law.
  • ISO/IEC 27001 certification assesses conformity of the system with the standard and does not automatically replace KSC obligations.

What does the organisation receive?

  • an applicability assessment explaining its status and scope,
  • a map of services, processes, systems, assets and suppliers,
  • a matrix of requirements, evidence, gaps and risks,
  • a readiness heatmap and management decision list,
  • an action roadmap with priorities, owners and deadlines,
  • a plan for ISMS implementation, exercises, training and system sustainment.

We can also conduct a KSC readiness audit for organisations outside the Act’s formal scope that wish to strengthen cyber resilience or meet customer and supply-chain requirements. We have prepared a separate page for healthcare entities: KSC in healthcare (in Polish).

For the wider diagnostic portfolio, see LeanTrix external audits.

KSC READINESS – GAPS – PRIORITIES

What is our role?

Our role – connecting requirements, technology and actual processes

LeanTrix delivers this service with subject-matter support from QualiTeam. We combine process management, standardisation, organisational change and capability development with expertise in management systems, ISO/IEC 27001, auditing and technology. This ensures cybersecurity extends across the organisation rather than remaining solely within IT.

We conduct the KSC readiness audit with management, service and process owners, IT/OT, security, purchasing, maintenance, HR, administration, communications and the data protection officer, as appropriate to the organisation. We work with actual processes and evidence rather than declarations.

During the project, we:

  • hold a management kick-off and agree the audit mandate, scope and criteria,
  • assess the entity’s applicability and relevant deadlines,
  • conduct interviews, observations, document reviews and dependency-mapping workshops,
  • analyse services, processes, IT/OT assets, data, locations and the supply chain,
  • compare KSC/NIS2 requirements with actual conditions and available evidence,
  • assess risks and the proportionality of technical and organisational measures,
  • examine incident management, continuity and recovery processes,
  • run a scenario exercise revealing gaps in decisions, escalation and communication,
  • prioritise recommendations by impact, urgency, effort and dependencies,
  • present management with a report, heatmap, roadmap, owners and proposed KPIs.

An assessment independent of technology sales

We do not sell security hardware or licences. Recommendations therefore follow risk and process needs rather than a product catalogue. A readiness audit does not automatically include penetration testing. We select technical testing according to risk and agree it separately to avoid disrupting systems, particularly OT environments and critical services.

Where implementation is needed, we help build the ISMS, documentation, roles, risk-treatment plan, incident processes, business continuity, supplier requirements, training and evidence package. If the goal is a statutory KSC audit or ISO/IEC 27001 certification, we prepare the organisation for independent assessment and maintain separation of roles.

Lead expert and implementation team

For systems and technology, we work with Dr Ścibór Sobieski, an expert in strategy, management systems and IT, and co-founder and CEO of QualiTeam. We adapt the team to the entity’s profile: a manufacturing company with OT, digital service provider, public body, logistics company, research organisation and infrastructure entity require different audits.

We conclude with a joint management review. Alongside findings, we agree the action sequence, responsibilities, required resources, progress measures and conditions for moving to implementation. The goal is a system that continues working after the project.

A handful of facts

0
months to fulfil obligations for entities within scope, as a general rule
0
hours for an early warning of a significant incident
0
years: maximum statutory audit cycle for an essential entity

Implementation support

We provide support based on the Kata process, which allows us to adapt our activities to the specifics of your organization, taking into account the jointly set goals. The Kata process consists of four key elements that enable effective implementation of assumptions.

Determining the course of action

Designing a concept that responds to the organization's goals and challenges.

Determining the current state

Learning about the current situation and collecting input data to define the next step.

Determining the target state

Determining the desired and measurable end result and a plan for its implementation.

Experiments - consultations

Implementation of activities in accordance with the established cooperation model, based on PDCA cycles.

We operate according to PDCA

P

PLAN

PLAN – applicability, scope and audit plan

In PLAN, we establish which requirements actually apply to the organisation. We begin the KSC readiness audit with its status, services and risks rather than a ready-made document checklist.

  • analyse sector, activities, legal form, size, related entities and specific statutory criteria,
  • establish whether the organisation is an essential entity, important entity, public entity or outside the formal scope,
  • verify listing obligations and registration, implementation and audit deadlines,
  • identify regulated services and the processes affecting their delivery,
  • create an initial map of IT/OT systems, data, assets, locations and suppliers,
  • agree reference criteria: KSC, NIS2, applicable implementing legislation, sector requirements and, as support, ISO/IEC 27001,
  • collect documentation, registers, test results, contracts, logs and other evidence,
  • agree risk criteria, a maturity scale and reporting with management,
  • schedule interviews, observations, workshops and safe technical verification.

PLAN produces an audit-scope charter: what we examine, against which criteria, with whom, using which evidence, and which systems and processes require particular care.

D

DO

DO – auditing actual practice and testing readiness

In DO, we move from documents to practice. We verify how the organisation manages cybersecurity in everyday work and whether evidence supports its declared controls.

  • interview management, service owners, IT/OT, security and support functions,
  • map the relationship between service, process, system, asset, supplier, risk and control,
  • review the ISMS, policies, procedures, instructions, risk registers, decisions and operational records,
  • examine management of access, MFA, assets, vulnerabilities, changes, updates, logs and monitoring,
  • verify physical security and the connections between IT and OT environments,
  • analyse contracts and supplier, cloud, servicing and outsourcing management,
  • examine backups, recovery test results, BIA, BCP, contingency plans and DR,
  • run an incident exercise covering decisions, escalation, communication and the 24-hour / 72-hour / 1-month reporting path,
  • assess cyber hygiene, management training and the capabilities of people in key roles,
  • record gaps, risks, evidence and recommendations in one audit worksheet.

We do not perform intrusive tests without agreement. Where a penetration test, vulnerability scan or OT test is justified by risk, we propose it as a clearly defined additional element.

C

CHECK

CHECK – assessing compliance, effectiveness and maturity

In CHECK, we compare requirements with documented reality. We distinguish missing documentation from an ineffective safeguard because they require different responses.

  • assess each requirement as met, partially met, unmet or outside the scope,
  • verify evidence quality and whether measures are implemented, used, monitored and tested,
  • check the completeness of the service, asset, supplier and risk-owner map,
  • assess whether safeguards are proportionate to incident likelihood and impact,
  • analyse management’s readiness for decisions, funding, oversight and crisis communication,
  • verify detection, escalation and response times and the ability to meet reporting deadlines,
  • check actual service-recovery capability rather than the existence of backups alone,
  • distinguish critical gaps, quick corrective actions and projects requiring funding,
  • create a readiness heatmap by KSC/NIS2 area and risk level,
  • review findings with process owners before reporting to management.

The CHECK report explains what is missing, the gap’s consequences, the evidence required, who should own the action and what must be done first.

A

ACT

ACT – implementation roadmap, accountability and sustainment

In ACT, we turn results into a feasible programme. We prioritise recommendations according to risk, applicable deadlines, dependencies, required resources and expected effect.

  • prepare actions for days 0–30 and 31–90, alongside longer-term systemic projects,
  • assign owners, deadlines, budgets, measures and closure criteria for each gap,
  • establish a RACI model for management, service owners, security, IT/OT and support functions,
  • design or update the ISMS, governing documentation and required operational records,
  • plan risk treatment, incident exercises and continuity and recovery testing,
  • clarify supplier requirements, contracts, supply-chain risk assessments and exit plans,
  • develop training for management, staff and specialist roles,
  • create an evidence index and a preparation plan for inspections, statutory audits or voluntary ISO/IEC 27001 certification,
  • establish KPIs, management-review routines and an annual improvement cycle,
  • support rollout to further processes, locations or group companies.

ACT closes the first PDCA cycle and starts the next. The organisation gains an action sequence, clear responsibilities and a mechanism for sustaining cyber resilience as technology, suppliers, processes and threats change.

Want to learn more? Contact us!

    Name and surname *
    Email address *
    Phone number *

    What are you interested in? *

    Additional message (optional)

    * required fields


    Our clients

    Wedel
    Geberit
    Viessmann
    Lajkonik
    Sumito Electric
    Tarczyński
    Autoliv
    Stadler
    UPM Raflatac
    Jost
    BSH
    Danone
    e-obuwie
    Kompania Piwowarska
    Recaro
    Tenneco
    Titanx
    ABM Leantrix Lean Management TWI Toyota Kata TOC
    Amazon Leantrix Lean Management TWI Toyota Kata TOC
    blum Leantrix Lean Management TWI Toyota Kata TOC
    Ikano Leantrix Lean Management TWI Toyota Kata TOC
    Kruk Leantrix Lean Management TWI Toyota Kata TOC
    Lincoln electronic Leantrix Lean Management TWI Toyota Kata TOC
    Sanden Leantrix Lean Management TWI Toyota Kata TOC
    Serpol Leantrix Lean Management TWI Toyota Kata TOC
    Stock Leantrix Lean Management TWI Toyota Kata TOC
    Velux Leantrix Lean Management TWI Toyota Kata TOC

    Our Customers' Opinions